
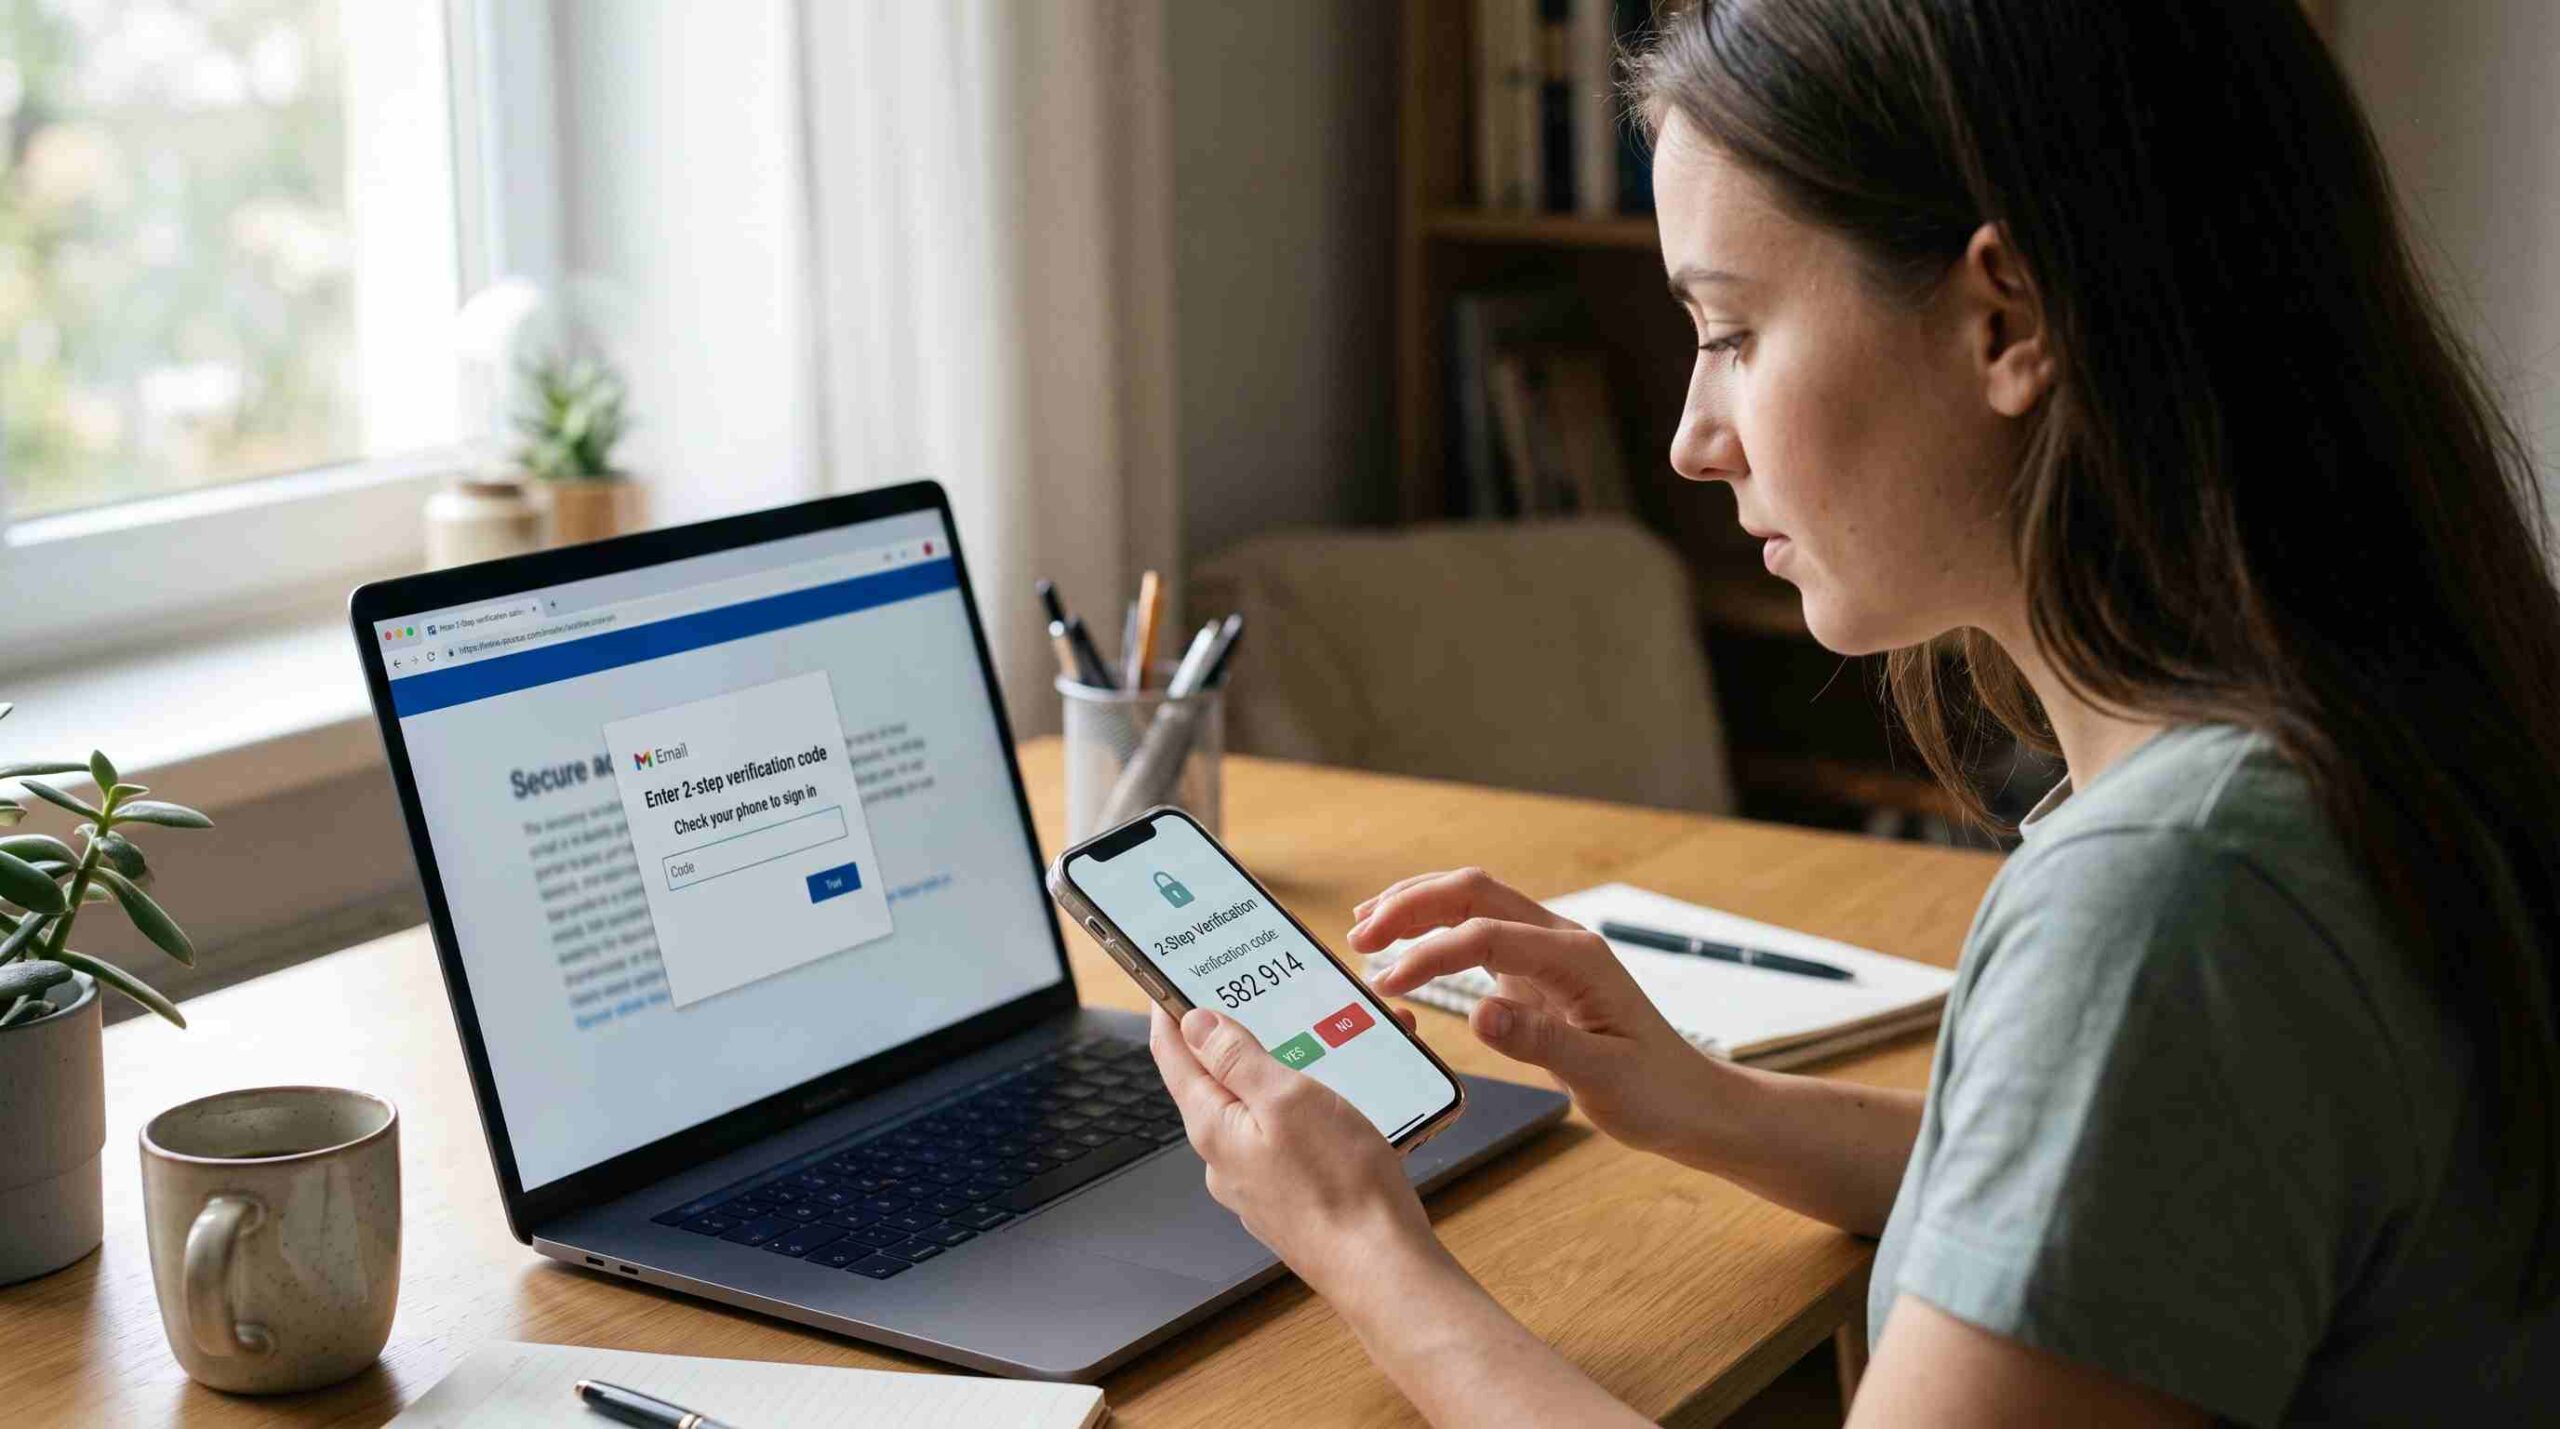
If you’ve ever logged into an account and been asked for a code sent to your phone right after typing your password, you’ve already used two-factor authentication. Understanding what is two-factor authentication and how does it work is one of the simplest ways to protect your online accounts from hackers. It takes only a few minutes to set up.
What Is Two-Factor Authentication?
So, what is two-factor authentication and how does it work in practice? Two-factor authentication, often shortened to 2FA, is a security process that requires you to prove your identity in two separate ways before you can access an account. A single password can be stolen, guessed, or leaked in a data breach. 2FA asks for a second piece of evidence that only you should have.
This second factor is usually something you physically possess, like your phone, or something unique to your body, like a fingerprint. The Cybersecurity and Infrastructure Security Agency (CISA) notes that multi-factor methods like this can block the vast majority of automated account-takeover attempts, even when a password has already been compromised.
How Does Two-Factor Authentication Actually Work?
Picture the login process as two separate checkpoints. The first checkpoint is your password, which falls under “something you know.” The second checkpoint comes from a different category entirely, so even if someone steals your password, they’re stopped at the second gate.
Here’s a typical flow: you enter your username and password as usual. The website doesn’t log you straight in. Instead, it asks for a second piece of proof. This might be a six-digit code texted to your phone, a push notification you approve on an authenticator app, or a physical security key you tap. Only after both steps succeed does the account unlock.
This works well because of simple math. A hacker would need to steal both your password and your phone (or your fingerprint, or your security key) at the same time. That’s far harder than just guessing or buying a leaked password online.
The Three Factors Behind Two-Factor Authentication
Security experts generally group authentication methods into three categories, and 2FA always combines two of them.
Something you know covers passwords, PINs, and security questions. Something you have includes your smartphone, a hardware token, or a smart card. Something you are refers to biometrics like a fingerprint, face scan, or voice pattern.
A real two-factor setup always pulls from two different categories. Two passwords, for example, don’t count as 2FA because they’re both “something you know.” The National Institute of Standards and Technology (NIST) publishes digital identity guidelines explaining why mixing categories produces much stronger security than stacking similar ones.
Common Types of Two-Factor Authentication
Now that you know what is two-factor authentication and how does it work on a conceptual level, it helps to see the common forms it takes.
SMS codes are the most familiar type. A text message delivers a one-time code to your phone. They’re convenient but slightly weaker than other methods, since attackers can sometimes intercept texts through SIM-swapping scams.
Authenticator apps, such as Google Authenticator or Authy, generate a fresh code every 30 seconds directly on your device. They don’t need a cell signal to work. Because the code never travels over a network, this method is considerably harder to intercept.
Push notifications send an approval request straight to your phone’s screen. You simply tap “yes” or “no.” This feels faster than typing a code and still holds up as highly secure.
Hardware security keys, like a YubiKey, are small physical devices you plug in or tap. Security teams consider them one of the strongest forms of 2FA because a remote attacker can’t fake physical possession of the object.
Biometric verification uses your fingerprint, face, or retina as the second factor. People often combine it with a device they already own, like a phone.
Why Two-Factor Authentication Matters
Passwords alone are no longer enough. Data breaches have exposed billions of login credentials over the years, and many people still reuse the same password across multiple sites. Once one account is compromised, attackers often try that same password everywhere else, a tactic known as credential stuffing.
This is exactly where understanding what is two-factor authentication and how does it work becomes practical rather than theoretical. Even if your password shows up in a breach, a second factor stands between the attacker and your account. Google’s own security research found that a simple phone-based second step blocked the overwhelming majority of automated bot attacks and targeted phishing attempts against real accounts.
2FA also gives you an early warning system beyond blocking hackers outright. If you suddenly receive an authentication prompt you didn’t request, that’s a strong signal someone has your password and is trying to break in. You get a chance to change it immediately.
How to Set Up Two-Factor Authentication
Setting up 2FA is usually quick and follows a similar pattern across most platforms.
Start by opening your account’s security settings, usually found under “Security” or “Login & Security.” Next, look for an option labeled “Two-Factor Authentication,” “2-Step Verification,” or “Multi-Factor Authentication.” Choose your preferred method, whether that’s an authenticator app, SMS, or a hardware key. Scan the QR code or enter the verification code to confirm the setup. Finally, save your backup codes somewhere safe in case you ever lose access to your second factor.
Most major services, including email providers, banks, and social media platforms, support at least one form of 2FA. Turning it on for your email account is the best place to start if you’ve been wondering what is two-factor authentication and how does it work well enough to actually use it. Email is often the gateway to resetting passwords on everything else.
Final Thoughts on Two-Factor Authentication
Two-factor authentication is a simple idea with a powerful effect at its core. It makes your accounts dramatically harder to break into by requiring two different kinds of proof instead of one. You now understand what is two-factor authentication and how does it work, from the categories of factors to the common methods available. You’re in a good position to turn it on across your important accounts today.
A password alone was never meant to be your only line of defense. Adding that second step costs you a few seconds at login but can save you from the much longer, much more painful process of recovering a hacked account.




